Category Publications

Postselection-loophole-free Bell test under strict spacetime constraints

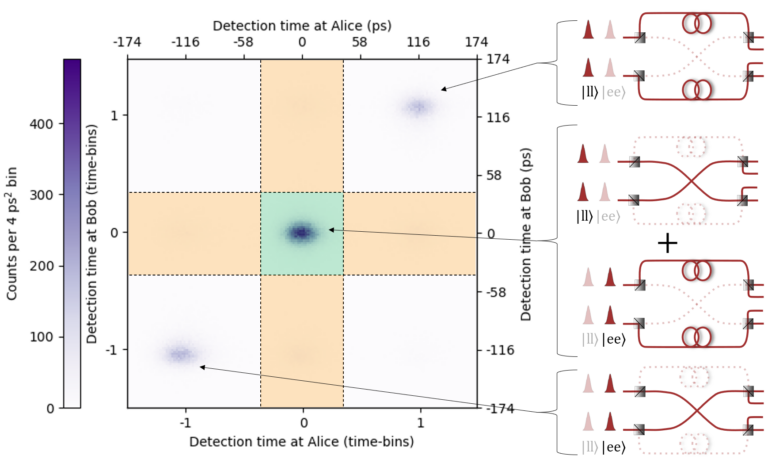
Entanglement gives rise to correlations between distant quantum systems that cannot be explained by local realistic theories. Bell inequality violations provide a direct way to reveal these correlations and certify nonlocality, especially when the relevant experimental loopholes are closed. Time-bin encoding, in which quantum information is encoded into well-defined temporal modes, is a commonly used platform for distributing photonic entanglement in optical fibers. Yet loophole-free Bell tests with time-bin entanglement have received comparatively little attention, owing in part to the postselection loophole introduced by conventional interferometric measurements. Here, we demonstrate a fiber‑based platform for Bell tests with time-bin entanglement that simultaneously closes the locality, freedom-of-choice, and postselection loopholes. We observe a CHSH violation of $S=2.583 \pm 0.002$, exceeding the local‑realistic bound by over 265 standard deviations. Notably, this rigorous certification of nonlocality is achieved at a separation distance of $49.0\pm0.7$~m, substantially shorter than previous photonic Bell tests addressing comparable space-time constraints. Beyond its foundational significance, our results demonstrate time‑bin entanglement as a viable route towards practical device‑independent quantum communication and a future quantum internet.
Multiplexing of CV and DV QKD Systems over Fibered and Free-Space Channels and Squeezed- and coherent-state quantum key distribution over a deployed hybrid fibre-free-space channel

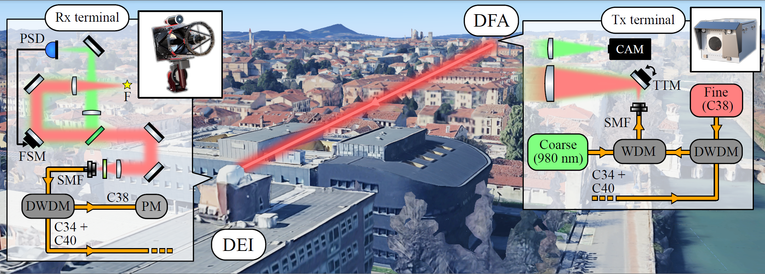
Future quantum communication infrastructures will need to serve heterogeneous users on shared physical channels: short-range, high-throughput links favor Continuous-Variable Quantum Key Distribution (CV-QKD), while long-reach, high-loss links remain the domain of Discrete-Variable QKD (DV-QKD). Wavelength-division multiplexing (WDM) of the two protocols on a common channel would address both regimes simultaneously, but their markedly different noise sensitivities make coexistence non-trivial and, to date, experimentally untested. Here we report the first simultaneous operation of two independent CV- and DV-QKD systems on a common optical channel, using standard C-band DWDM filters at 1550.12 nm (CV) and 1545.32 nm (DV). We demonstrate joint operation on both optical fiber and a 620 m urban daylight free-space link. On fiber, the two systems exhibit the expected complementarity, crossing over at 7.56 dB of channel loss where both deliver ∼1.43 Mbit/s; in daylight free-space, both sustain Mbit/s key rates under time-varying atmospheric attenuation. Across all configurations we observe no measurable multiplexing-induced penalty in QBER or excess noise. These results establish hybrid CV-DV WDM as a practical building block for heterogeneous quantum communication networks, where metropolitan high-throughput users and long-reach backbone links can be served on a single physical infrastructure.

Quantum bounds and device-independent security with rank-one qubit measurements

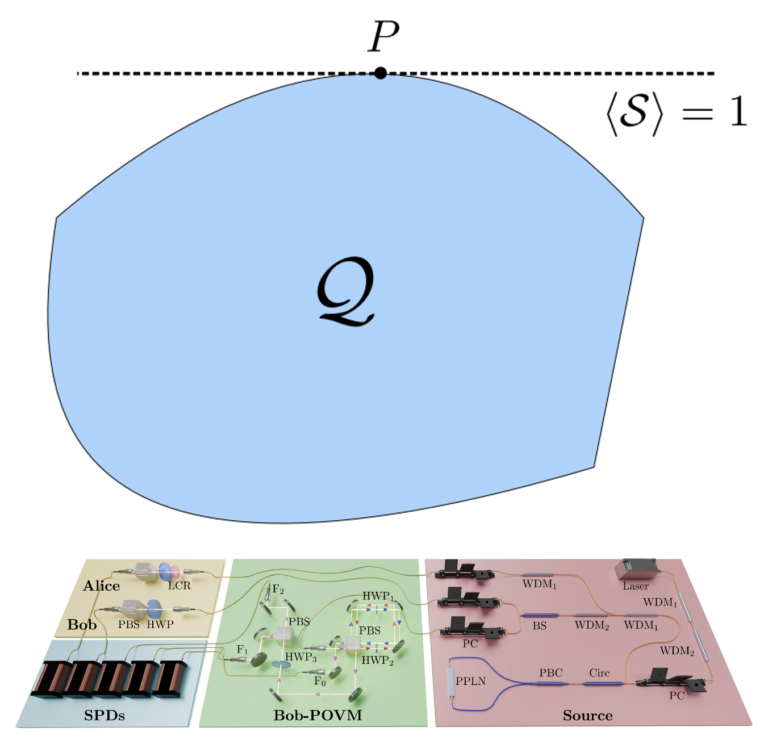
Device-independent (DI) quantum protocols use Bell inequality violations to ensure security or certify quantum properties without assumptions on the devices’ internal workings. In this work, we study the role of rank-one qubit positive operator-valued measures (POVMs) in DI scenarios. This class includes all qubit extremal POVMs, i.e., those measurements that cannot be realized as mixtures of others, as well as part of non-extremal POVMs, recently shown to be useful in sequential quantum protocols. We demonstrate that any rank-one POVM can generate correlations in bipartite scenarios that saturate a Tsirelson inequality when two parties share an arbitrary entangled two-qubit state and perform specific self-tested measurements. For extremal POVMs, such saturation enables explicit computation of guessing probability and worst-case conditional von Neumann entropy. From the Tsirelson inequality, we establish a randomness certification method that facilitates numerical simulations and we validate it through a proof-of-concept experiment with three-outcome POVMs and tilted entangled states.

High-performance heterodyne receiver for quantum information processing in a laser-written integrated photonic platform

Continuous variable quantum key distribution (CV-QKD) and continuous variable quantum random number generation (CV-QRNG) are critical technologies for secure coContinuous variable quantum key distribution (CV-QKD) and continuous variable quantum random number generation (CV-QRNG) are critical technologies for secure communication and high-speed randomness generation, exploiting shot-noise-limited coherent detection for their operation. Integrated photonic solutions are key to advancing these protocols, as they enable compact, scalable, and efficient system implementations. We introduce femtosecond laser micromachining (FLM) on borosilicate glass as a platform for producing photonic integrated circuits (PICs) realizing coherent detection suitable for quantum information processing. Employing off-chip detectors, we exploit the specific features of FLM to produce a PIC designed for CV-QKD and CV-QRNG applications. The PIC features fully adjustable optical components that achieve precise calibration and reliable operation under protocol-defined conditions. The device exhibits low insertion losses (≤1.28dB), polarization-insensitive operation, and a common-mode rejection ratio exceeding 73 dB. These characteristics allowed the experimental realization of a source-device-independent CV-QRNG with a secure generation rate of 42.74 Gbit/s and a quadrature phase-shift-keying-based CV-QKD system achieving a secret key rate of 3.2Mbit/s. Our results highlight the potential of FLM technology as an integrated photonic platform, paving the way for scalable and high-performing quantum communication systems.

High-speed source-device-independent quantum random number generator on a chip

A wide range of applications require, by hypothesis, to have access to a high-speed, private, and genuine random source. Quantum random number generators (QRNGs) are currently the sole technology capable of producing true randomness. However, the bulkiness of current implementations significantly limits their adoption. In this work, we present a high-performance source-device-independent QRNG leveraging a custom-made integrated photonic chip. The proposed scheme exploits the properties of a heterodyne receiver to enhance security and integration to promote spatial footprint reduction while simplifying its implementation. These characteristics could represent a significant advancement toward the development of generators better suited to meet the demands of portable and space applications. The system can deliver secure random numbers at a rate greater than 20 Gbps with a reduced spatial and power footprint.

Experimental post-selection loophole-free time-bin and energy-time nonlocality with integrated photonics

Time-bin encoding has been widely used for implementing quantum key distribution (QKD) on optical fiber channels due to its robustness with respect to drifts introduced by the optical fiber. However, due to the use of interferometric structures, achieving stable and low intrinsic Quantum Bit Error rate (QBER) in time-bin systems can be challenging. A key device for decoy-state prepare & measure QKD is represented by the state encoder, that must generate low-error and stable states with different values of mean photon number. Here we propose the MacZac (Mach-Zehder-Sagnac), a time-bin encoder with ultra-low intrinsic QBER (<2e-5) and high stability. The device is based on nested Sagnac and Mach-Zehnder interferometers and uses a single phase modulator for both decoy and state preparation, greatly simplifying the optical setup. The encoder does not require any active compensation or feedback system, and it can be scaled for the generation of states with arbitrary dimension. We experimentally realized and tested the device performances as a stand-alone component and in a complete QKD experiments. Thanks to the capacity to combine extremely low QBER, high stability and experimental simplicity, the proposed device can be used as a key building block for future high-performance, low-cost QKD systems.

Low-error encoder for time-bin and decoy states for quantum key distribution

Time-bin encoding has been widely used for implementing quantum key distribution (QKD) on optical fiber channels due to its robustness with respect to drifts introduced by the optical fiber. However, due to the use of interferometric structures, achieving stable and low intrinsic Quantum Bit Error rate (QBER) in time-bin systems can be challenging. A key device for decoy-state prepare & measure QKD is represented by the state encoder, that must generate low-error and stable states with different values of mean photon number. Here we propose the MacZac (Mach-Zehder-Sagnac), a time-bin encoder with ultra-low intrinsic QBER (<2e-5) and high stability. The device is based on nested Sagnac and Mach-Zehnder interferometers and uses a single phase modulator for both decoy and state preparation, greatly simplifying the optical setup. The encoder does not require any active compensation or feedback system, and it can be scaled for the generation of states with arbitrary dimension. We experimentally realized and tested the device performances as a stand-alone component and in a complete QKD experiments. Thanks to the capacity to combine extremely low QBER, high stability and experimental simplicity, the proposed device can be used as a key building block for future high-performance, low-cost QKD systems.

Geometry of sequential quantum correlations and robust randomness certification

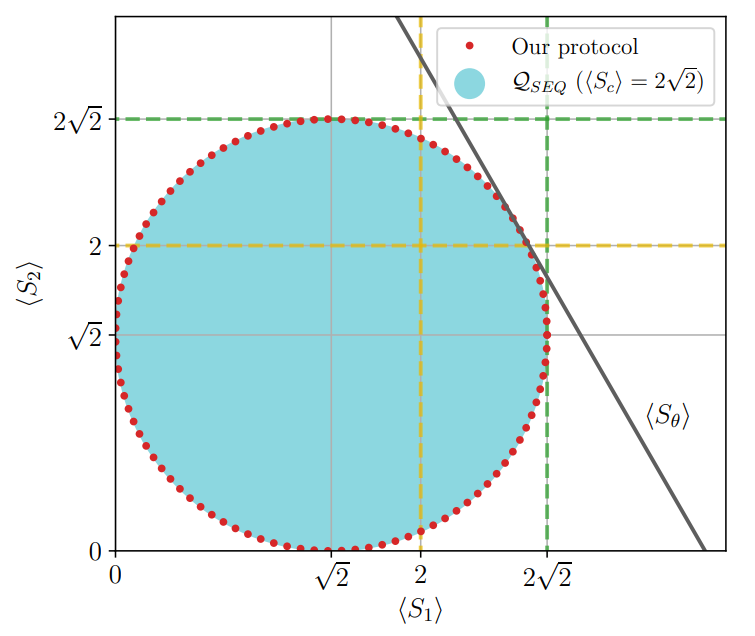
Quantum correlations between the measurements of two or more separated observers play a fundamental role in many applications, such as randomness generation or key distribution. Recently, it was realized that sequential measurements (i.e., defined with a precise temporal ordering between subsequent measurements on a given system) can enhance the performance of these protocols. However, the theoretical understanding of how to maximize this performance is limited and the relation with the boundary of quantum correlations is unexplored. In the case of one party on one side and two sequential parties on the other, we study the geometry of quantum correlations and its implications for robust device-independent randomness generation. We identify a boundary for the set of these correlations expressed as a trade-off between the amount of nonlocality between different observers and show that this allows to generate the maximum possible device-independent randomness in our setting, namely two bits. We propose a practical protocol based on non-projective measurements that can produce the boundary correlations under ideal conditions, and address its robustness to noise, showing that it is improved compared to previous approaches. Finally, we implement our protocol in a proof-of-concept experiment based on a photonic implementation. With the obtained correlations we could certify more bits per state with respect to the standard CHSH protocol, proving that our protocol is feasible and robust to real-world imperfections. Our work paves the way for a full understanding of sequential quantum correlations and their exploitation for practical and efficient device-independent protocols.

Deployment-ready quantum key distribution over a classical network infrastructure in Padua

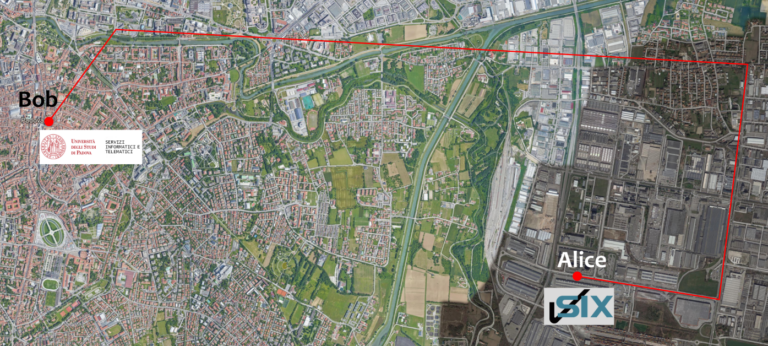
Current technological progress is driving Quantum Key Distribution towards a commercial and world widescale expansion. Its capability to deliver unconditionally secure communication will be a fundamental feature in the next generations of telecommunication networks. Nevertheless, demonstrations of QKD implementation in a real operating scenario and their coexistence with the classical telecom infrastructure are of fundamental importance for reliable exploitation. Here we present a Quantum Key Distribution application implemented overa classical fiber-based infrastructure. By exploiting just a single fiber cable for both the quantum and the classical channel and by using a simplified receiver scheme with just one single-photon detector, we demonstrate the feasibility of low-cost and ready-to-use Quantum Key Distribution systems compatible with standard classical infrastructure.

Security bounds for decoy-state QKD with arbitrary photon-number statistics

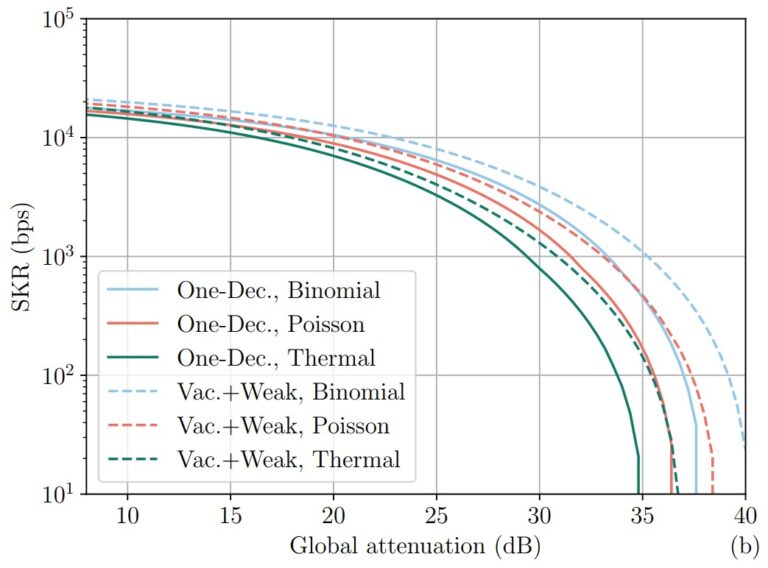
The decoy-state method is a standard enhancement to quantum key distribution (QKD) protocols that has enabled countless QKD experiments with inexpensive light sources. However, new technological advancements might require further theoretical study of this technique. In particular, the decoy-state method is typically described under the assumption of a Poisson statistical distribution for the number of photons in each QKD pulse. This is a practical choice, because prepare-and-measure QKD is often implemented with attenuated lasers, which produce exactly this distribution. However, sources that do not meet this assumption are not guaranteed to be compatible with decoy states. In this work, we provide security bounds for decoy-state QKD using a source with an arbitrary photon emission statistic. We consider both the asymptotic limit of infinite key and the finite-size scenario, and evaluate two common decoy-state schemes: the vacuum+weak and one-decoy protocols. We numerically evaluate the performance of the bounds, comparing three realistic statistical distributions (Poisson, thermal, binomial), showing that they are all viable options for QKD.